)
)
Anti-Money Laundering Knowledge Hub
Guidance and resources for the new AML framework legislation
Introduction
The EU AML Package comprises the Anti-Money Laundering Regulation (AMLR), the Sixth Anti-Money Laundering Directive (AMLD6), the Regulation establishing the Anti-Money Laundering Authority (AMLA), and the Wire and Crypto asset Transfer Regulation (WCTR). Together, these measures represent the most significant reform of the EU’s AML/CFT framework to date, replacing fragmented national regimes with a harmonised, directly applicable Single Rulebook and enhanced EU level supervision.
Timeline
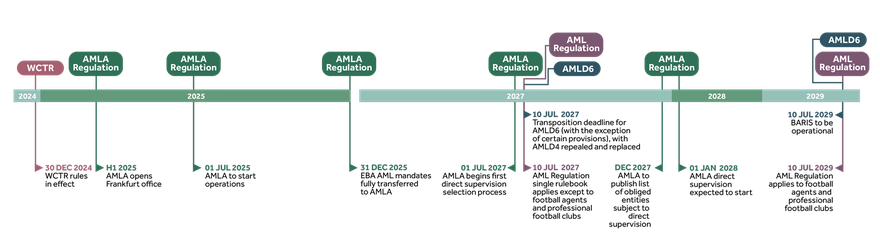
With one year to go until 10 July 2027, the EU AML Package is entering its final design phase, after which firms will have regulatory certainty as to the detailed operational requirements they must meet by July 2027.
)
Latest Q&As
The EU AML package is a set of new EU laws which aim to provide greater harmonisation, consistency and centralised oversight to the EU AML regime.
The AML/CFT package consists of the following:
AMLD6 (Directive 2024/1640): AMLD6 repeals and replaces the earlier AMLD5 (Directive 2018/843) and AMLD4 (Directive 2015/849). The majority of its provisions will need to be transposed into national law by 10 July 2027.
AML (Regulation 2024/1624): This Regulation, known as AMLR or the Single Rulebook, has the aim of reducing discrepancies in national implementation of AML/CFT rules by introducing a directly applicable and uniform set of rules. Similar to AMLD6, this Regulation will apply from July 2027.
AMLAR (Regulation 2024/1620): This Regulation, known as AMLAR, establishes the Authority for Anti-Money Laundering and Countering the Financing of Terrorism (AMLA). The Authority is based in Frankfurt and commenced operations in 2025.
Wire and Crypto‑asset Transfer Regulation (WCTR): The WCTR applies to firms, including crypto‑asset service providers (CASPs), where such firms initiate, execute, receive or intermediate wire transfers, or crypto‑asset transfers.
The new framework will be applied on a staggered basis as follows:
the AMLD6 must be transposed by EU Member States into national law by 10 July 2027, with certain provisions (primarily in relation to beneficial ownership registers) to be transposed beforehand;
the AMLR becomes applicable on 10 July 2027, with sector-specific provisions taking effect by 10 July 2029; and
the AMLAR officially entered into force on 26 June 2024, and the operations of AMLA commenced on 1 July 2025. AMLA will commence direct supervision of selected obliged entities on 1 January 2028.
With under one year to go until 10 July 2027, the EU AML Package is entering its final design phase, after which firms will have regulatory certainty as to the detailed operational requirements they must meet by July 2027. By 10 July 2026, AMLA must finalise and submit to the European Commission the full set of technical standards required under the EU AML Package.
Yes, UCITS, EU AIFs and their EU regulated management companies (UCITS management companies and AIFMs) will fall within scope of the new framework as “obliged entities”.
Firms in-scope under the AML package are listed as “obliged entities” under AMLR and include:
credit institutions;
financial institutions, such as insurance undertakings, insurance intermediaries, investment firms under MiFID II, UCITS, EU AIFs, EU regulated management companies (UCITS management companies and AIFMs), credit intermediaries for mortgage and/or consumer credit, central securities depositories, bureaux de change, financial holding companies and EU/ third-country branches of EU financial institutions;
entities which carry on any of the financial activities listed in Annex I of CRD (for example, lending on its own account, factoring, financial leasing, providing guarantees, and operating as part of a financing business);
trust or company service providers;
non-financial mixed activity holding companies;
crypto-assets service providers; and
professionals, such as auditors, external accountants and tax advisors and notaries, lawyers and other independent legal professionals when providing certain transactional activities.
AMLA is the European Authority for Anti-Money Laundering and Countering the Financing of Terrorism, a union body which was established on 26 June 2024 in Frankfurt, Germany. AMLA commenced its operations on 1 July 2025.
One of the main tasks of AMLA will be the direct supervision of up to 40 selected obliged entities that pose the highest degree of cross border ML/TF risk which is expected to start in January 2028. Each selected obliged entity should be active in at least six member states and deemed high risk using AMLA’s risk criteria. AMLA will conduct periodic assessments of credit and financial institutions in order to determine who is eligible. The selection of obliged entities will be reviewed every 3 years.
In addition to its direct supervisory role, AMLA will perform a range of EU‑level functions, including developing a harmonised supervisory framework, monitoring ML/TF risks within the EU, reviewing the performance of national competent authorities (NCAs), coordinating supervisory colleges, maintaining a central AML database and FIU.net, requiring NCAs to take supervisory action where necessary, and issuing technical standards and guidelines.
The Central Bank of Ireland (CBI) will no longer be the primary AML supervisor for certain high‑risk, cross‑border institutions selected for direct supervision by AMLA. However, the CBI will remain the day‑to‑day AML supervisor for the vast majority of obliged entities in Ireland, including domestic firms and smaller or lower‑risk entities.
The introduction of the Single Rulebook under the AMLR, which sets out uniform EU rules with the aim of establishing a harmonised and consistent approach to AML/CFT will also mean that there will be little opportunity for the CBI to exercise discretion or variation when supervising compliance by firms regulated by it with the new framework. AMLR sets out uniform EU rules with the aim of establishing a harmonised and consistent approach to AML/CFT across the EU. As a consequence, limited provision is made for national interpretation of those EU rules.
Under AMLR, customer due diligence measures (CDD) must be applied in certain circumstances, including when:
establishing a business relationship;
carrying out an occasional transaction of at least €10,000 in a single operation or through linked transactions. Under the current regime, CDD must be applied for occasional transactions of €15,000 or more (outside certain sector-specific thresholds);
carrying out a transfer of funds of €1,000 or more; or
carrying out an occasional cash transaction of at least €3,000. This represents a new, specific threshold for cash transactions and is distinct from the general €10,000 threshold applicable to other occasional transactions.
Separate thresholds for the application of CDD apply to crypto‑asset providers and gambling service providers.
AMLR is a fundamental re‑engineering of the CDD framework, which retains core concepts from AMLD4/5 but significantly expands, formalises and operationalises those requirements. For example, under AMLR,
the volume and granularity of CDD data that must be collected, verified, and continuously processed is increased;
specific rules are introduced for multi-layered and complex structures;
the treatment of beneficial owners is brought much closer to that of the customer, in terms of identification, verification, PEP screening and ongoing monitoring;
new granular harmonised rules are introduced for each of standard, simplified and enhanced due diligence;
sanctions screening is now explicitly embedded as a mandatory element of CDD, rather than sitting alongside it as a parallel obligation;
expanded data collection requirements are introduced;
customer data must be kept up to date and a defined refresh period must apply, namely 1 year for high risk customers and 5 years for all other customers; and
CDD will be extended to include: (i) persons acting on behalf of the customer (e.g. authorised representatives or intermediaries etc); and (ii) persons on whose behalf or for whose benefit transactions are conducted (i.e. the underlying principals and nominators). Item (ii) is known as the expanded “look-through” approach. The “look-through” approach is a key point of concern for the funds industry.
AMLR introduces a longer and more comprehensive definition of beneficial ownership. Under AMLR, it is now clear that ownership and control must always be assessed in parallel.
Under AMLR, beneficial owners of a legal entity are natural persons who either (i) hold a direct or indirect ownership interest of 25% or more, calculated across all levels of the ownership structure, or (ii) exercise control over the entity, whether through majority ownership, voting rights, the ability to appoint or remove management, veto or decision‑making rights, profit or asset distribution rights, or other means such as agreements, family relationships or nominee arrangements. AMLR also provides for the ownership threshold to be lowered in higher‑risk sector. AMLR allows the European Commission to lower that threshold, potentially to 15%, for higher‑risk categories of entities, where dilution of ownership could otherwise frustrate effective transparency.
Under the current AML/CFT framework, Member States maintain central registers containing information on the ultimate beneficial owners of legal entities and certain trusts. However, the existing regime does not require systematic disclosure of all layers of ownership or control.
AMLD6 strengthens this framework by enhancing the scope and quality of information recorded, including a specific requirement to identify and record nominee arrangements. This reflects a clearer ‘look‑through’ approach to ownership and control.
AMLD6 also reforms access to central registers by replacing broad public access with a controlled access regime. Full access is retained for competent authorities, Financial Intelligence Units (FIUs) and obliged entities for CDD purposes, while the public access regime is restricted to persons demonstrating a legitimate interest, subject to defined safeguards.
Finally, AMLD6 further harmonises the registration of non‑EU trusts by promoting consistent application of existing registration triggers across member states and improving the functionality, traceability and interoperability of central registers.
These new rules in relation to the beneficial ownership registers and access thereto must be transposed into Irish law prior to the deadline set out in AMLD6 (namely by 10 July 2026). The public‑access regime adopted in Ireland is more restrictive than that set out in AMLD6.
While the AMLR does not fundamentally change the PEP regime, it clarifies and harmonises the definition of PEPs across the EU and extends PEP screening, where relevant, to natural persons on whose behalf or for whose benefit a transaction or activity is carried out (i.e. the underlying principals) in line with a broader look‑through approach.
The AMLR formalises compliance functions by requiring the appointment of both a compliance manager and a compliance officer. The compliance manager, at senior management level, is responsible for overseeing AML/CFT compliance and ensuring that policies, procedures and controls are implemented and aligned with the entity’s risk profile.
The compliance officer, appointed by the management body and operating independently, is responsible for the day‑to‑day operation of AML/CFT controls, including maintaining AML policies and procedures, reporting suspicious transactions to the FIU, and acting as the primary liaison with regulators. In the Irish funds context, this role broadly corresponds to the Money Laundering Reporting Officer (MLRO).
Under AMLR, obliged entities remain required to implement appropriate AML/CFT training and to ensure that relevant personnel are competent to perform their functions. Under the new framework, these obligations are clarified and applied more consistently across the EU, including to persons in comparable positions, such as agents and distributors.
The AMLR strengthens and harmonises the group‑wide AML/CFT framework by imposing more prescriptive requirements across the EU. In particular, obliged entities must establish and implement group‑wide AML/CFT policies, procedures and controls (including for branches and subsidiaries in third countries) and conduct initial and ongoing group‑wide risk assessments.
Where a group has a non‑EU parent and more than one obliged entity in the EU, the AMLR requires that responsibility for group‑wide AML/CFT compliance is anchored in a designated EU‑based entity within the EU sub‑group.
The AMLR also broadens the scope of entities treated as financial institutions, including certain holding and mixed‑activity holding companies, with the result that some entities previously outside the formal framework may now fall within scope.
)
Final Reports on RTS submitted to the European Commission by AMLA
briefing | Financial Regulation
Find out more)
AMLD6 and Beneficial Ownership Central Registers: New Access Rules in Ireland
briefing | Financial Regulation
Find out more)
Publication of Ireland’s first National AML, Countering the Financing of Terrorism and Countering Proliferation Financing Strategy
briefing | Financial Regulation
Find out more1 of 3

)
Who We Advise
Our dedicated AML team provides a comprehensive service for firms and funds operating in the financial services sector including:
)
)
UCITS Management Companies and AIFMs
)
Administrators and other Fund Service Providers
)
Investment Firms
)
Banks
)
Insurers
)
Trading Platforms
)
Non-Bank Lenders
)
Payments Firms
)
Crypto Asset Service Providers
Contact a member of the team for further information
)
Get in touch to discuss the new AML framework
Our team can guide you through the latest legislation and what it means for your organisation.
)
)
)
)
)